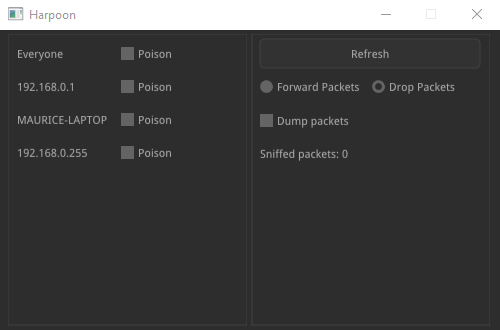
Harpoon - Yet another ARP posioning tool
After having started to use libraries like libpcap or WinDivert, I got curious about low-level networking protocols like Ethernet, IP, ICMP, ARP, TCP or UDP. Especially the Address Resolution Protocol (ARP) fascinated me, as I have previously used tools like Ettercap or Cain & Abel to experiment with Man-in-the-middle attacks using ARP poisoning, however, I did not know how ARP poisoning worked in detail. Basically, using an ARP request, you can request the MAC address of a particular host behind a local IPv4 address. You will then receive an ARP response containing the MAC address from that host. ...